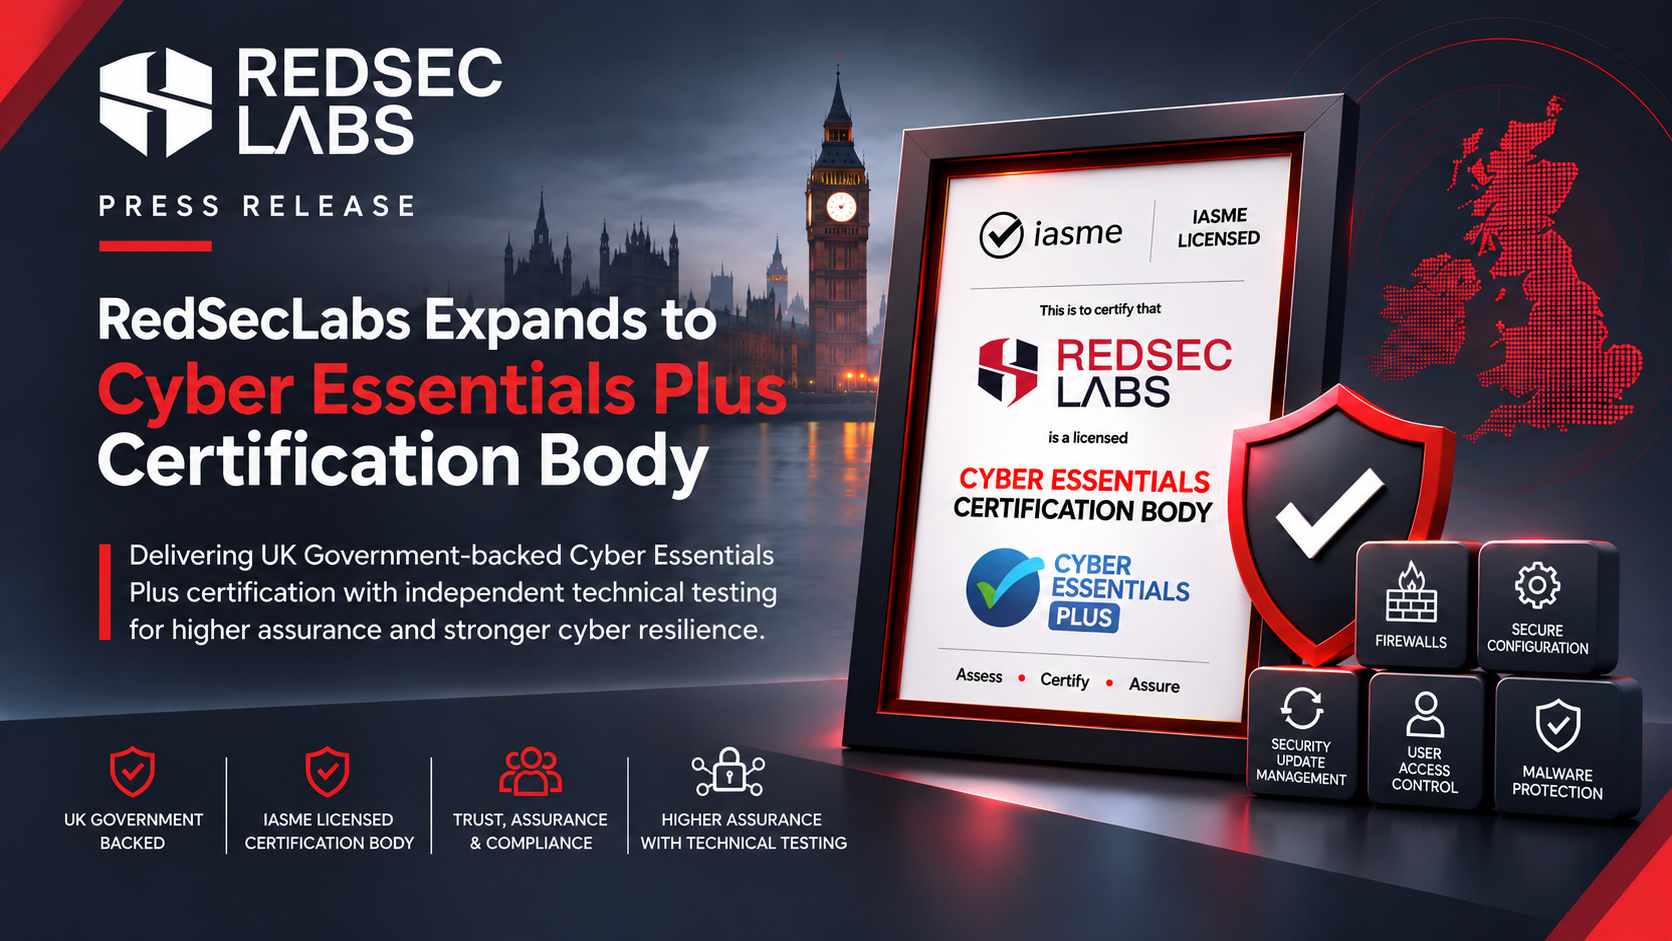
The London-headquartered cybersecurity consultancy strengthens its UK assurance practice with Cyber Essentials Plus assessment and certification capabilities, extending its existing IASME-licensed Cyber Essentials services.
LONDON, 04/11/2026 — RedSecLabs, an independent cybersecurity consultancy serving regulated and security-conscious organisations, today announced the expansion of its certification capabilities to include Cyber Essentials Plus, enabling the company to conduct independent technical assessments under the UK Government-backed Cyber Essentials scheme.
The development builds on RedSecLabs' appointment as an IASME-licensed Cyber Essentials Certification Body in August 2026 and represents another milestone in the company's continued investment in UK cybersecurity assurance.
Cyber Essentials Plus is the higher-assurance level of the Cyber Essentials scheme, supported by the UK's National Cyber Security Centre (NCSC) and delivered through IASME. Unlike the standard Cyber Essentials certification, which relies on a verified organisational self-assessment, Cyber Essentials Plus requires independent technical testing to confirm that essential security controls are effectively implemented.
With this expanded capability, RedSecLabs can support organisations seeking independently validated assurance of their cybersecurity controls through the Cyber Essentials Plus certification process.
Moving Beyond Self-Assessment to Independent Technical Verification
Both Cyber Essentials and Cyber Essentials Plus assess five fundamental cybersecurity controls: firewalls, secure configuration, security update management, user access control and malware protection.
Cyber Essentials Plus provides additional assurance through technical testing of an organisation's systems and a representative sample of its devices.
The assessment includes vulnerability scanning, verification of software security updates, evaluation of endpoint security configurations and testing of malware protection mechanisms.
These activities help establish whether the controls described during the initial Cyber Essentials assessment are operating effectively across the organisation's IT environment.
For RedSecLabs, the expansion reflects its existing technical security expertise and its focus on helping organisations translate security requirements into demonstrable protection.
“Cyber Essentials establishes an important baseline, but organisations also need confidence that their security controls are working as intended,” said Rafay Baloch, Founder and CEO of RedSecLabs.
“Expanding our capabilities to Cyber Essentials Plus allows us to provide that additional level of independent technical assurance. It also brings together our experience in penetration testing, vulnerability assessment and compliance assurance within a recognised UK certification framework.”
“Our objective is to help organisations move beyond demonstrating that security policies and controls exist, towards independently verifying that those controls are effectively implemented.”
Expanding RedSecLabs’ Independent Cybersecurity Assurance Capabilities
The addition of Cyber Essentials Plus builds on RedSecLabs' established portfolio of security assessment and assurance services.
RedSecLabs is a CREST member and PCI DSS Qualified Security Assessor (QSA) company, providing penetration testing, red teaming, security advisory, SWIFT Customer Security Programme assessments and specialised compliance assurance services.
The company also holds UKAS-accredited ISO/IEC 27001:2022 and ISO 9001:2015 certifications, demonstrating its commitment to information security management and quality management.
By extending its Cyber Essentials certification capabilities to include Plus, RedSecLabs further strengthens its ability to support organisations across different levels of security assurance, from foundational cybersecurity certification to advanced technical security testing and industry-specific compliance assessments.
Supporting Stronger Cybersecurity Assurance Across UK Organisations
Cyber Essentials and Cyber Essentials Plus are widely recognised within the UK cybersecurity landscape, particularly among organisations operating in government supply chains, regulated sectors and security-conscious commercial environments.
Cyber Essentials Plus provides organisations with independently tested evidence of their implementation of the scheme's five technical controls.
As part of its expanded certification offering, RedSecLabs will conduct Cyber Essentials Plus assessments through qualified assessors in accordance with the applicable IASME scheme requirements.
The capability will enable RedSecLabs to work with organisations seeking to validate their security controls, meet relevant contractual certification requirements and demonstrate a stronger level of cybersecurity assurance to customers and stakeholders.
This development reinforces RedSecLabs' continued commitment to expanding its UK assurance practice and delivering independent, technically grounded security assessments.
About RedSecLabs
RedSecLabs is a London-headquartered cybersecurity consultancy providing penetration testing, red teaming, incident response, security advisory and compliance assurance services to organisations across financial services, payments, healthcare, SaaS and the public sector.
RedSecLabs is an IASME-licensed Cyber Essentials Certification Body, CREST member and PCI DSS Qualified Security Assessor company, and holds ISO/IEC 27001:2022 and ISO 9001:2015 certifications.
The company operates internationally, with a presence in the United Kingdom, United States and United Arab Emirates.
RedSecLabs was founded by Rafay Baloch, a cybersecurity researcher and practitioner recognised for his work in browser and application security.
Media Enquiries
RedSecLabs
Website: https://www.redseclabs.com
Telephone: +44 20 3996 1505